
Latest
Security
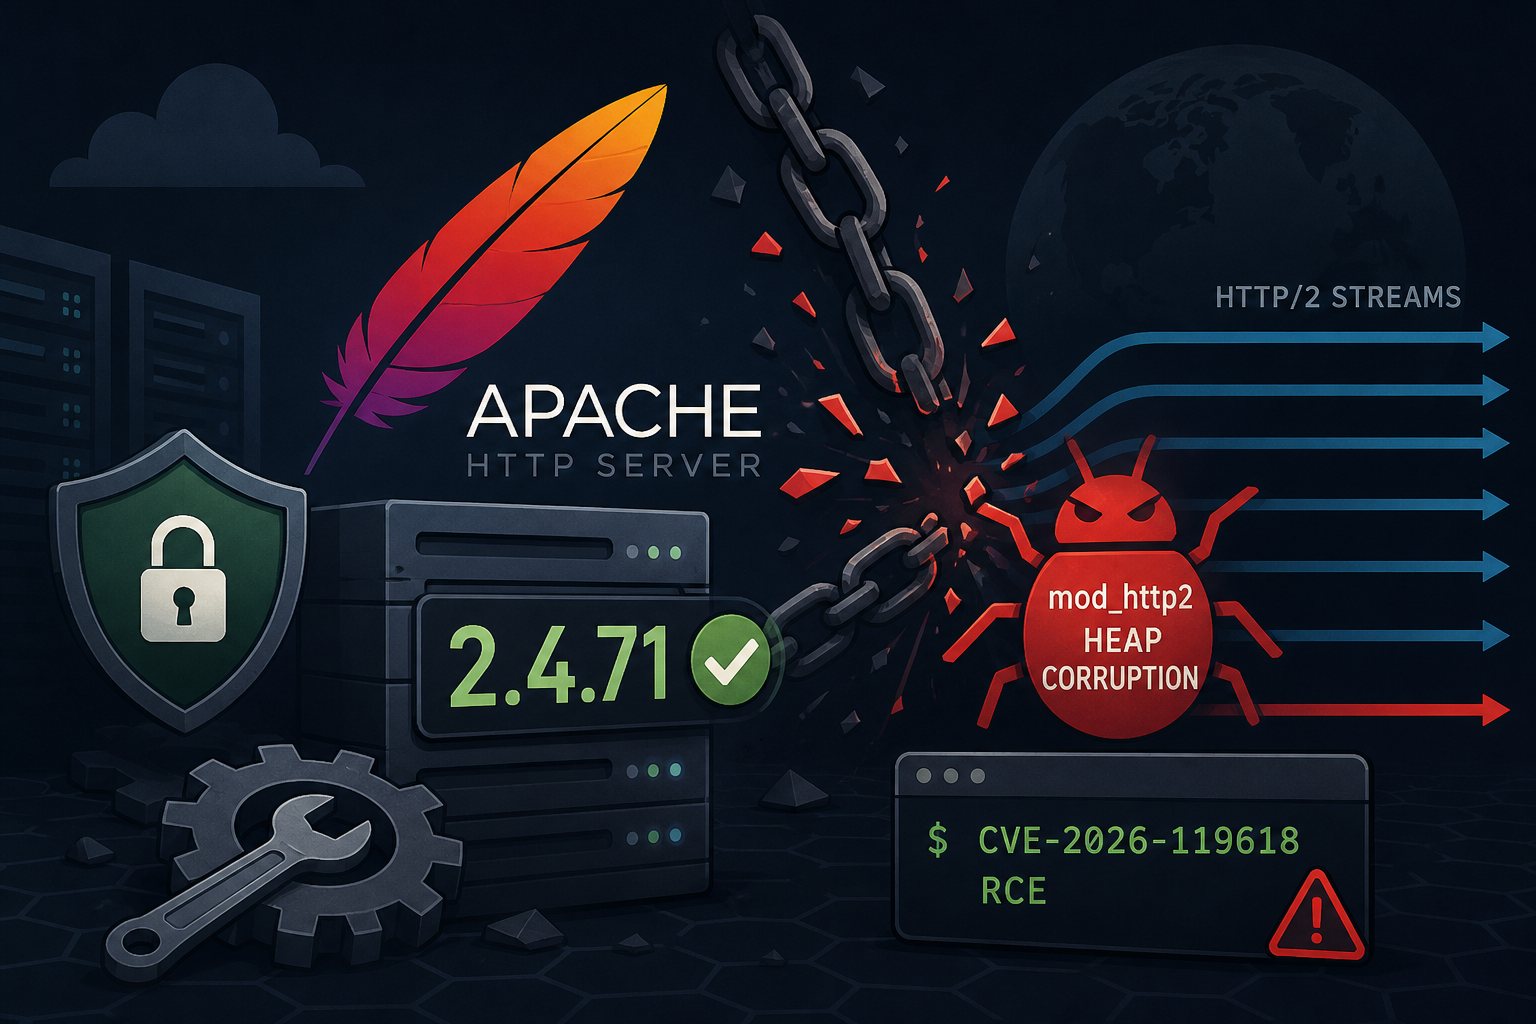
CVE-2026-119618: Apache 2.4.71 fixes unauthenticated HTTP/2 RCE
Apache httpd 2.4.55 through 2.4.70 with HTTP/2 enabled can be taken over remotely through a mod_http2 thread-safety bug. Fixed packages are out for RHEL 9, RHEL 10 and Debian 13; Ubuntu has none yet.
Read article